September 23, 2026
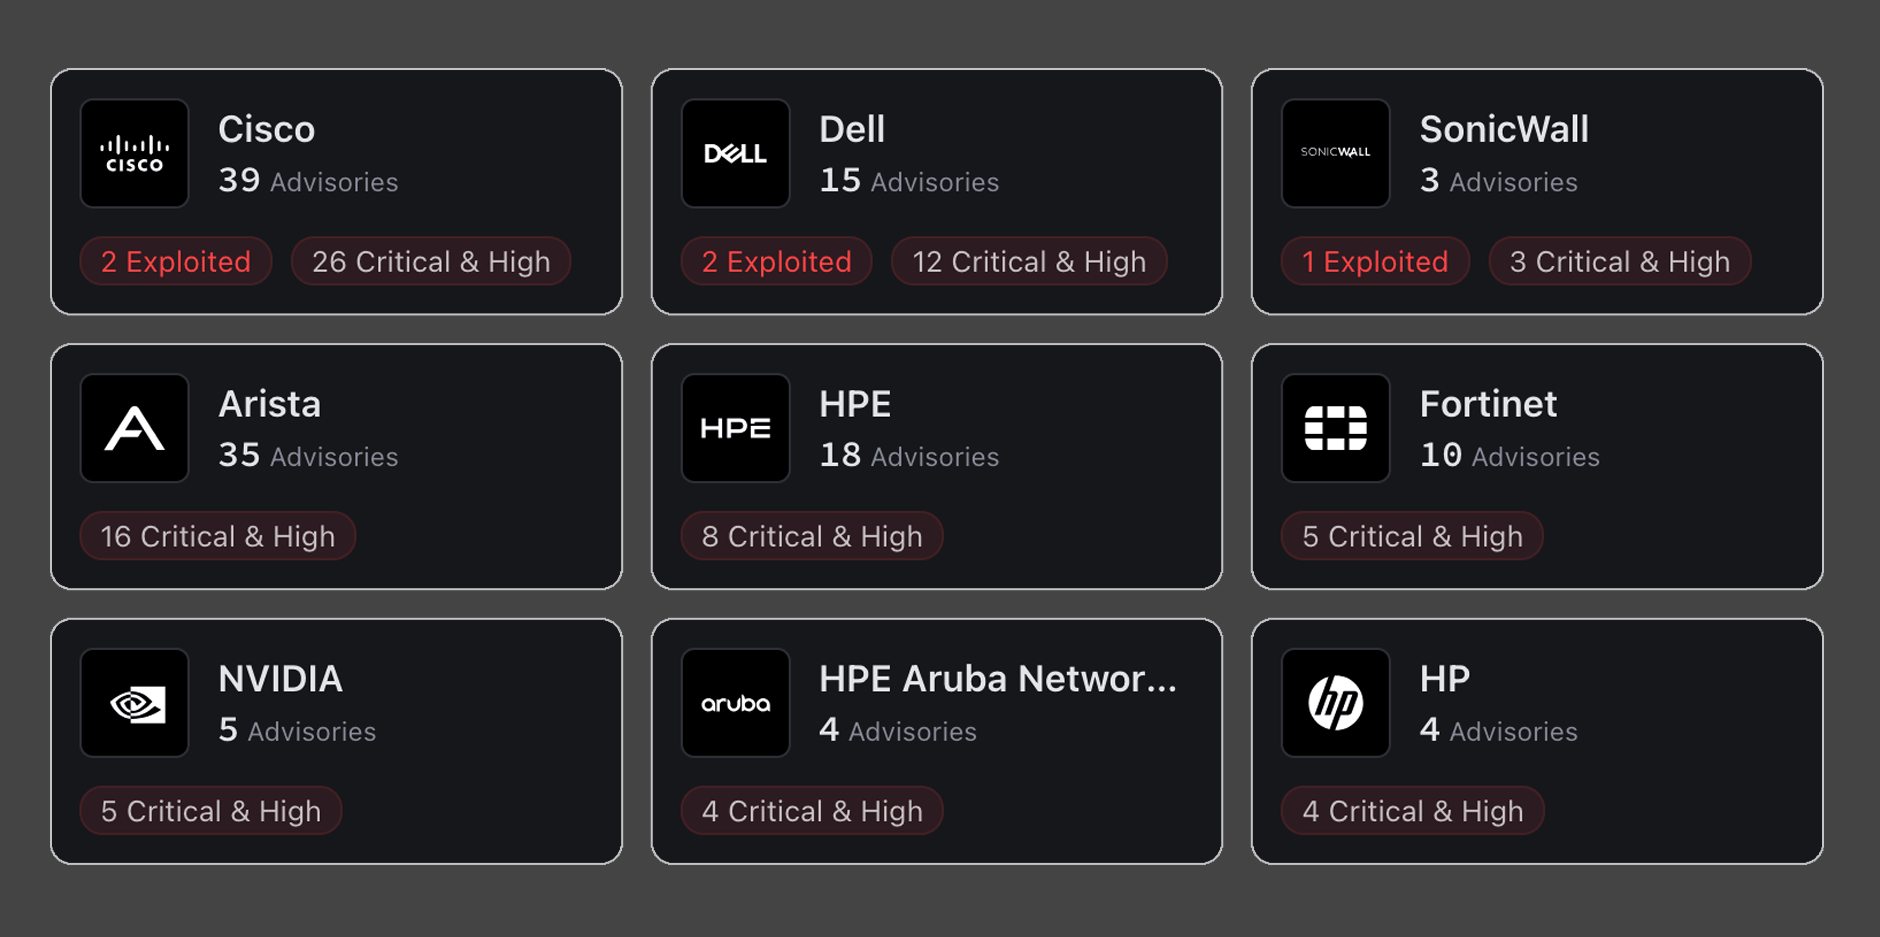
The third InfraTrust Pulse finds the management plane under attack for a second straight month, and patching alone does not mitigate the risk. You still need to threat hunt on impacted devices. From August 25 through September 17, we tracked 158 new security advisories across 17 vendors. CVSS flags 42 as critical, but 71 are remotely exploitable with no authentication, and that is the figure that should drive remediation. Your top priority is Cisco Secure Firewall Management Center (CVE-2026-20079, CVSS 10.0), added to KEV September 9, with Cisco confirming exploitation since August. The hardening release supersedes the August hotfix, so apply it even if you already patched. Next, patch Cisco ISE (CVE-2026-76460, CVSS 10.0), exploited before its advisory was published, and SonicWall SMA 1000 (SNWLID-2026-0016), where an unauthenticated SSRF (CVE-2026-83548, CVSS 10.0) chains to command injection and SonicWall recommends re-imaging. After that, the critical gear included Arista EOS (two at 10.0), Cisco Nexus 9000 and Check Point VPN (both 9.8), and firmware fixes from AMI, Cisco, Dell, and Lenovo for the UEFI Shell Secure Boot bypass Eclypsium disclosed.